Managed Hosting / Redmine Products / Redmine Passwords Plugin for online teams
What if your team could organize passwords securely right in the project?
Manage your business passwords centrally, clearly and securely, right where your project management happens. With the team password manager for Redmine, company-wide.
Team password manager for Redmine
The Redmine Passwords Plugin is a team password manager right inside Redmine. You manage access data and passwords centrally and clearly in Redmine and share them easily and securely with your colleagues.
Who is it for?
For teams that already work with Redmine and share access data per project:
- Agencies: access to customer websites, hosting and tools, neatly separated per customer project.
- IT and operations: servers, network devices and business software in one place.
- Development teams: access to test, staging and production environments.
- Projects with customers: customers hand over access data securely instead of sending it by email.
Why in Redmine? The passwords live with the project and are linked to issues. The same roles and permissions apply as in the rest of Redmine. When someone joins or leaves the project, access changes automatically. You do not need a second tool with its own user management.
For personal passwords with automatic filling in the browser, a personal password manager remains the better choice.
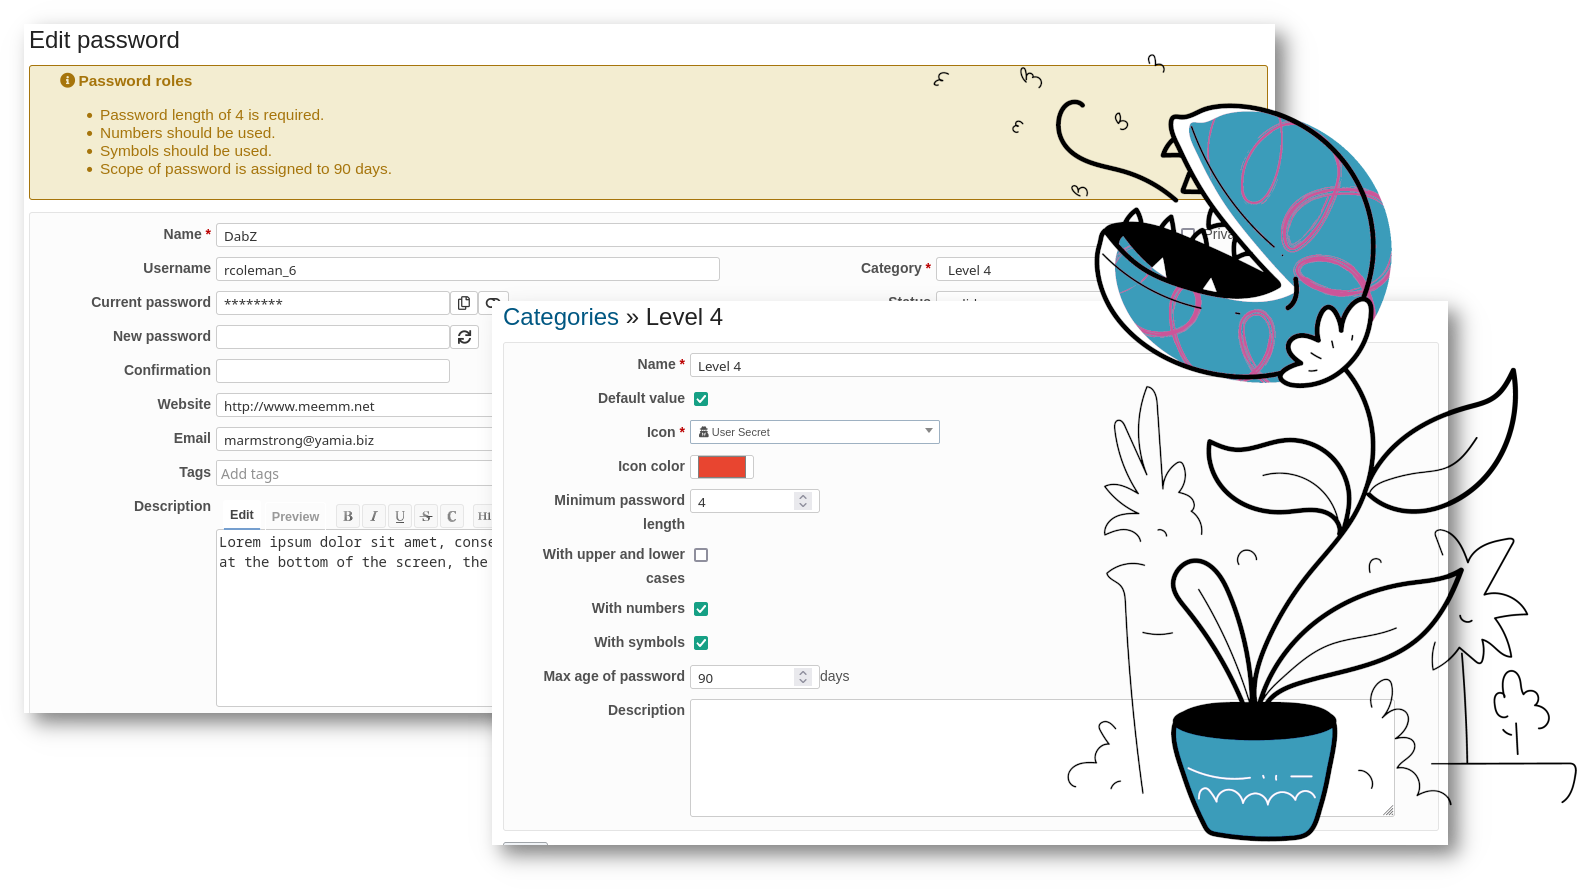
Simple and secure to use.
Redmine’s proven encryption (AES-256-CBC) keeps your data safe. Redmine’s role-based permission and access management makes secure administration and sharing easy. A password generator that follows the rules of each category helps you create safe passwords. You copy password and username with one click.
Encryption method
For maximum compatibility with newer Redmine versions, the plugin uses Redmine’s own encryption. It requires a key (database_cipher_key) in the Redmine configuration. Once it is set, password and description of every new entry are stored encrypted in the database automatically, and existing entries are converted once by a script. You can change the key when needed: decrypt the passwords by script, set the new key and encrypt again. Redmine’s own encrypted fields are handled the same way (rake db:decrypt and db:encrypt). The encryption standard is the Advanced Encryption Standard (AES-256-CBC).
Password rules that think along
Every password belongs to a category, for example Server, Email or Customer access. The category defines what a good password is:
- Rules: minimum length, upper and lower case, digits and symbols. The generator follows them.
- Password strength: Redmine shows whether a password is weak, ok, strong or very strong, and points out on the detail page when an entry breaks the rules of its category.
- Maximum age: Per category you set how long a password is valid. The detail page then shows how many days it remains valid.
- Status: Every password is valid, to verify or invalid. Filters quickly find everything that needs renewing.
- History: Every change is recorded, without storing old passwords.
Good to know before you buy
- Secure login: Redmine offers two-factor login. That protects the passwords too.
- When someone leaves the team: Access ends with the project membership. The passwords stay in the project.
- Backup: The passwords are part of the normal Redmine backup. Back up the key as well. Without it, the backup cannot be read.
- Customers and partners: External people get a restricted role. They only see the passwords of their project. Private entries only if they are assigned to them.
- Export: A CSV or XLSX export can contain passwords in clear text. That is why it has its own role permission.
- What the plugin is not: no browser extension that fills in login forms. And no log of who viewed a password.
Improve productivity. Accelerate goals. Make your team happy.
Our goal is to deliver a high quality product with real added value to demanding customers. Change your daily work with Redmine, now.

Why customers like Redmine Passwords
- It is safe. A central place to store and share access data securely. Password and description are stored encrypted (AES-256-CBC) in the database.
- It is simple. Central password administration and access to passwords.
- It is a team player. Built for teams. Authorized team members get to the passwords at any time, even when colleagues are away.
Product highlights
- Create, share and tag passwords per project and mark them as private
- Filterable, saveable lists, also across projects
- Encrypted storage (AES-256-CBC)
- Generator, category rules and password strength
- Links to issues, DB entries and contacts (with the DB or ServiceDesk plugin)
- CSV import, export with its own role permission
- Custom fields and change history
- Wiki macros and dashboard blocks, from v4.7.0 with the flexible chart block Chart: Passwords
Solves typical problems
- Passwords no longer sit openly in the project wiki.
- Nobody sends passwords by email or chat anymore.
- Only authorized project members see the passwords, administrators without membership do not.
- Security audit filters find weak and outdated passwords.
- Knowledge stays in the team, even when someone is away or leaves.
Why us? Our solutions are efficient, integrated, scalable, flexible and up-to-date. This way we not only make sure that your product or service is on target, but also help you to transfor your business.
Our development base is Munich (Germany). Documentation and support available in: EN, DE. Plugin: Multilingual. Plugin is also available as Cloud solution.
Learn more about the plugin requirements and read our FAQ before purchase.
Our plugins will suit your needs!
Our Redmine plugins are multilingual and a good choice if you want to work productively. 12 month support & updates included.
Buy Passwords Plugin v4.6.0
Affordable prices regardless of your team size